 PreShip
For founders building with Lovable, Bolt, Replit, v0 & Cursor
Launch-ready in 48 hours.
You built your app with AI. We check it for the mistakes AI tools make most — leaked keys, open databases, unprotected AI chat endpoints — and hand you the exact fixes, in plain English.
Launching soon. We are not taking payments or running scans yet — and we are not collecting a waitlist. Reach us at the address above.
- Read-only checks
- Deep checks only after ownership is verified
- $9.99 credited if you upgrade
We keep nothing readable: reports self-destruct after 24 hours.
- Critical OpenAI key visible in your website code
- Critical Customer table readable by anyone
- High AI chat endpoint open to the internet
- Fixed Ready-to-merge fix + re-scan passed
An October 2025 study by Escape.tech of 5,600 AI-built apps found 2,000+ high-impact vulnerabilities and 400+ exposed secrets. Most founders don't find out until a customer — or an attacker — does.
How it works
Prove it's yours
Add one line to your site (a file or a meta tag) so we know you own it. We never test sites without the owner's permission.
We review it
We check your live site, every JavaScript file it loads, your AI endpoints, and — if you connect them — your code, database and hosting settings.
You get the fixes
A clear report, copy-paste fixes (or a ready-to-merge code change), a re-scan to confirm, and a badge to show customers.
What we check
The issues that actually sink AI-built apps — explained without jargon.
Leaked keys
OpenAI, Stripe, Supabase admin and other secrets accidentally shipped in your website code.
Open databases
Supabase tables without Row Level Security and Firebase rules that let anyone read or write.
AI chat endpoints
Chat or completion routes anyone can call — running up your AI bill.
Exposed files
Public
.envfiles,.gitfolders and source maps that reveal your code.Security headers
Protection against clickjacking and script injection (CSP, HSTS and friends).
Hosting settings
Vercel previews left public and secret-looking
NEXT_PUBLIC_/VITE_variables.Your code
Committed secrets, missing auth on API routes and unsafe database clients — with a fix PR.
File storage
Storage buckets that make private user uploads downloadable by anyone.
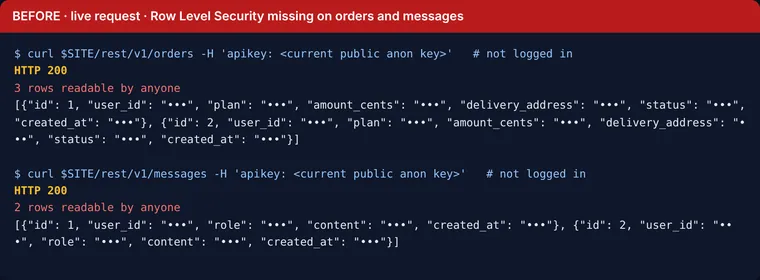
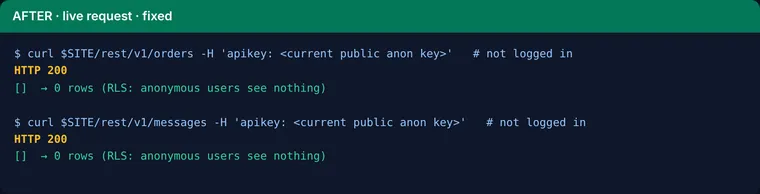
See a real before & after
Demo app MealMate is a fictional demonstration app we built and host locally — fake company, fake data, fake keys.
- Critical issues
- 9 → 0
- Issues resolved
- 18
- Time to fix
- One patch + re-scan
PreShip Basic Scan — $9.99
Paste your public app URL. You get your grade, issue counts by severity, and which areas need work. After checkout you'll verify you own the site (one file or meta tag) to unlock the database and exposed-file checks — or run passive checks only. Upgrade to the PreShip Launch Review anytime — your $9.99 is credited.
Scans open at launch. Email hello@preshipsecurity.com — no waitlist form.
Simple pricing
Start with a $9.99 PreShip Basic Scan, upgrade to the PreShip Launch Review with your $9.99 credited ($289.01), add monitoring after.
Basic Scan
A quick read-only health check.
- Security grade (A-F)
- Issue count by severity
- Which areas need work
- One scan per domain every 30 days
- $9.99 credited if you upgrade
Launch Review
Everything you need to launch safely.
- Full JS crawl incl. lazy chunks
- AI endpoint & LLM key checks
- Repo scan + ready-to-merge fix
- Copy-paste DB rules & headers
- Re-scan to verify
- Investor-ready PDF + trust badge (valid 90 days)
Guard
Stay safe as you ship.
- Weekly automated re-scans
- Email alerts on new issues
- Badge stays valid while Guard is active
- 1 site
Agency
For agencies & studios.
- Up to 15 client sites
- White-label reports
- Launch Review per new client app
- Priority support
Verified Audit
Launch Review + human expert review.
- Everything in Launch Review
- Manual review by a security specialist
- Call to walk through fixes
| What you get | Basic Scan $9.99 | Launch Review $299 | Guard $49/mo | Agency $199/mo |
|---|---|---|---|---|
| Security grade (A–F) | ✓ | ✓ | ✓ | ✓ |
| Every finding, explained | Counts & areas | ✓ | ✓ | ✓ |
| Copy-paste fixes & fix PR | — | ✓ | New issues | ✓ |
| Code, database & hosting checks | — | ✓ | Site checks | ✓ |
| Re-scan to verify | — | ✓ | Weekly | Weekly |
| PDF report & trust badge | — | Badge valid 90 days | Badge valid while active | White-label |
| Sites | 1 | 1 | 1 | 15 |
Our own security: we keep nothing readable
A security company shouldn't become your biggest risk. So PreShip is built to forget.
- Reports self-destruct after 24 hours. Each report is encrypted with its own key and deleted automatically.
- Your code is never kept. Repos, zips and scan data live in a temporary folder and are wiped after every job — even if it fails.
- Secrets are never stored. Keys we find are masked in reports; our logs are scrubbed of tokens.
- Minimal access. Read-only connections; tokens are discarded after your review unless you opt into Guard (encrypted, revocable anytime).
- What we do keep: your account, payment records (legally required) and a grade-only badge — grade, date, domain. No findings.
Questions founders ask
I'm not technical. Will I understand the report?
Yes. Every finding explains what's wrong, why it matters, and what to do, in plain English. Fixes are copy-paste, or a code change your developer (or AI tool) can apply in one click.
Lovable / Bolt / Supabase already have a security check. Why pay?
Built-in checks are a good start but look at one piece. We review the whole app as an outsider sees it — every JavaScript file, your AI endpoints, your database settings, and your code — then give you the fixes and re-scan to confirm.
Is this a penetration test or a compliance certificate?
No. PreShip is an automated security review. It is not a penetration test, a security audit, or a compliance certification (such as SOC 2 or HIPAA), and it can't guarantee your app is secure. It catches the common, high-impact mistakes AI-built apps make before launch.
Why do I have to verify I own my site?
Some checks go beyond what a normal visitor's browser loads — for example, testing whether your Supabase or Firebase data can be read with your public key, or whether your .env file can be downloaded. We run those only after you prove ownership by adding one file (/.well-known/preship.txt) or one meta tag, for both the Basic Scan and the Launch Review. Without verification, the Basic Scan runs passive checks only: your homepage, its security headers and the JavaScript it loads. If you verify later, you can re-run the same Basic Scan once with the full checks at no extra cost.
Will scanning break my app?
No. Our checks are read-only and rate-limited. We don't log in, submit forms, send prompts to your AI, or change data.
Do you store my secrets or code?
We keep nothing readable: reports (HTML, PDF, patch) are encrypted with a per-report key, delivered to you, and auto-deleted after 24 hours. Cloned repos, zip uploads, and scan working data live only in a temp dir and are wiped after each job. Secrets are never persisted; logs are redacted. We keep only your account, payment records, and a grade-only badge (grade, date, domain — no findings). Guard (opt-in) stores envelope-encrypted connection tokens you can revoke anytime.
What happens to my report after delivery?
We keep nothing readable: encrypted reports self-destruct after 24 hours. Download or email your copy promptly. Your public badge keeps only the grade, date, and domain.
How long is my badge valid?
A badge from a PreShip Launch Review is valid for 90 days after the review (or your latest re-scan). With PreShip Guard, it stays valid for as long as Guard is active, because we re-check your site every week. An expired badge says "expired" so visitors aren't misled.
What does "48 hours" mean?
Automated results are usually ready in minutes. We commit to 48 hours for the full Launch Review, including fixes and your re-scan.
What's the difference between PreShip Basic Scan and PreShip Launch Review?
The $9.99 PreShip Basic Scan tells you your grade, how many issues of each severity we found, and which areas they're in (for example "Exposed credentials" or "Database access controls"). The PreShip Launch Review shows every finding in full with exact fixes, checks your code and AI endpoints more deeply, and includes a re-scan, report and badge. Each domain gets one Basic Scan every 30 days.
If I upgrade, do I pay twice?
No. Your $9.99 Basic Scan is credited, so the Launch Review costs $289.01, as long as you upgrade within 60 days of buying the Basic Scan.
Which tools do you work with?
Apps built with Lovable, Bolt, Replit, v0, Cursor and similar — hosted anywhere. Optional read-only connections for GitHub, Supabase, Firebase and Vercel go deeper, or upload a zip of your code.
Who processes my payment?
Checkout is handled by Stripe. Stripe acts as the merchant of record through Link: it appears as the seller on your receipt, calculates and collects any sales tax or VAT, and handles receipts, refunds and disputes. We never see your card details.
For developers
- Secrets in HTML, entry bundles and lazy chunks (follows ES imports and Vite/webpack/Next manifests on the same origin)
- Supabase RLS exposure via PostgREST with your public anon key · Firebase RTDB/Firestore rules
- Exposed
.env,.git, source maps · security headers (CSP, HSTS, XFO, nosniff) - AI apps: LLM keys (OpenAI, Anthropic, Groq, OpenRouter, HF…) and unauthenticated
/api/chat-style routes — passive GET/OPTIONS only, never prompts - Repo scan with gitleaks + semgrep + built-in rules; fixes delivered as a PR-ready diff
GET /.well-known/preship.txt
preship-verify-3f9c…

POST /api/launch-review
{"url":"https://app.example","repo":"https://github.com/you/app",
 "authorize":true}